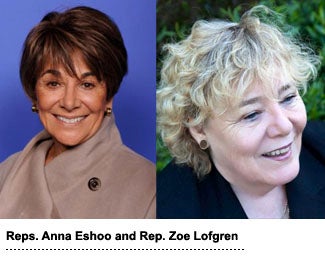
Two California House Democrats are taking a stab at federal privacy legislation with a bill that, if passed, would be more exacting than the California Consumer Protection Act (CCPA).
The Online Privacy Act of 2019 (HR 4978) was introduced on Tuesday by Democratic Reps. Anna Eshoo and Zoe Lofgren of California, who both represent parts of Silicon Valley.
The proposed law would establish an independent federal agency to enforce privacy protections and investigate abuses; create a set of user data rights a la Europe’s General Data Protection Regulation; require explicit consent in order to disclose or sell personal information; and place limitations on companies that use data to build behavioral profiles without consent.
[Click here to read the full text of the bill.]
Eshoo and Lofgren wrote the first draft of the Online Privacy Act in June and spent the next few months gathering feedback from academics and privacy advocacy groups, including the Electronic Privacy Information Center and Public Knowledge.
On a press call with reporters on Tuesday, Eshoo noted that the Online Privacy Act is “stronger” than the CCPA – and that’s by design.

There’s been support for federal privacy legislation on both sides of the aisle but little actual process. In the vacuum left by Congress’s inaction, multiple state privacy laws have cropped up, with CCPA being the strictest.
Although technology companies and advertising trade organizations have also pushed for federal privacy regulation, lawmakers are skeptical of their motives. One of the most popular lobbyist talking points is that a patchwork of state-based privacy laws will drive companies batty – and potentially out of business.
Democrats won’t support federal privacy legislation that preempts state laws if the legislation isn’t as stringent as the CCPA. In other words, they want CCPA to set the floor for a nationwide privacy law.
Eshoo and Lofgren’s proposal takes that notion to heart.
Here’s a selection of the most important provisions in the bill:
User rights: The bill would give users the right to access, correct, delete and transfer data about themselves, as well as the right to request a human review of any decisions made through the automated processing of personal information. Companies would be required to obtain opt-in consent before using data to inform machine learning or AI algorithms. The bill also introduces a new “right to permanence,” which would let users decide how long companies are allowed to keep their data.
Company obligations: Companies would be required to explain why they need the data they want to collect. They would not be allowed to keep personal information longer than necessary, disclose or sell it without explicit consent, use data to discriminate or use third-party data to re-identify individuals. Companies would also be barred from using private communications, such as emails and web traffic, for ads or “other invasive purposes.” Dark patterns that finagle consent would be verboten.
Enforcement: The Online Privacy Act would establish an independent federal agency called the Digital Privacy Agency (DPA) to enforce privacy protections and investigate abuses.
The DPA’s remit: This new federal agency would be able to issue regulations in order to implement the bill and levy fines for any violations. The maximum fine would be the same as the max fine in the FTC Act: $42,530 per incident. State attorneys general would be empowered to enforce the bill, which also includes a private right of action. That means individuals could sue for damages. The private right of action under the CCPA is limited to data breach-related violations.
Other bits and bobs: The bill also makes doxxing a criminal act, restricts companies from using data to build behavioral profiles without consent and exempts small businesses from “the most onerous requirements.” Small businesses are defined as entities that don’t earn revenue from the sale of personal information, earn less than half of their annual revenue from targeted advertising, maintain the personal info of fewer than 250,000 individuals, have fewer than 200 employees and make under $10 million in revenue.